CompTIA CS0-004 Actual Free Exam Questions – Full Free
CompTIA CySA+ CS0-004 Free Dump – Questions 1-20 with Answers
Free scenario-based CS0-004 dump questions for the CompTIA CySA+ certification exam. Each CS0-004 question includes the correct answer and a detailed explanation. Work through them as a diagnostic and spend your study time on the gaps they reveal.
CS0-004 Practice Questions 1-5
Question 1
Which of the following is the most important reason why tactics, techniques, and procedures (TTP) are beneficial to a defensive strategy?
A. TTP provides useful insights on the hash values and internet protocol addresses attributed to an attacker.
B. TTP provides useful insights on an attacker’s indicators of compromise.
C. TTP provides useful insights on the tools used by an attacker.
D. TTP provides useful insights on the strategy and behavior of an attacker.
Answer: D. TTP provides useful insights on the strategy and behavior of an attacker.
TTPs reveal attacker strategy and behavior, which is more valuable than static IoCs for defense.
Question 2
Which of the following is the best reason to heavily segment business-critical assets from within the network?
A. Legacy systems
B. Degraded functionality
C. Asset obfuscation
D. Proprietary server
Answer: A. Legacy systems
Legacy systems often lack modern security controls and require segmentation to reduce risk.
Question 3
A cybersecurity analyst receives an unstructured text document that contains advanced persistent threat (APT)-related indicators of compromise (IoCs). The analyst needs to extract the IPv4 addresses. Which of the following is the best tool to accomplish this task?
A. CyberChef
B. Wireshark
C. Zeek
D. Open Cyber Threat Intelligence (OpenCTI)
Answer: A. CyberChef
CyberChef is ideal for extracting and manipulating data like IPv4 addresses from unstructured text.
Question 4
Which of the following best describes why operational technology (OT) devices use compensating controls?
A. Industrial control systems use significant network bandwidth.
B. Outage windows are usually scheduled.
C. Traditional IT security solutions may not be compatible.
D. OT devices are typically not encrypted.
Answer: C. Traditional IT security solutions may not be compatible.
OT devices often cannot run standard IT security tools, so compensating controls are used.
Question 5
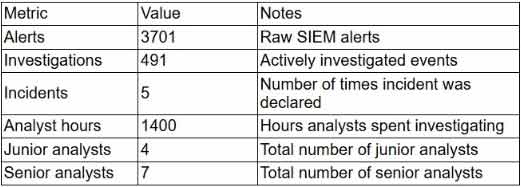
The Chief Information Security Officer (CISO) reviews the following security operations metrics from the last month:
Which of the following is the best action to improve overall security operations efficiency?
A. Leverage a cloud security posture management tool to add asset context to alerts.
B. Analyze and tune the detections that are causing non-actionable alerts.
C. Implement playbooks for the junior analysts to use during investigations.
D. Perform internal incident training on the most common alerts from security information and event management (SIEM).
Answer: B. Analyze and tune the detections that are causing non-actionable alerts.
Tuning detections reduces non-actionable alerts and improves SOC efficiency.
CS0-004 Practice Questions 6-10
Question 6
A public threat intelligence report includes indicators of compromise (IoCs) for threat actors. The threat actors are exploiting a zero-day vulnerability that the vendor has not fixed. Which of the following techniques should be used until a patch is available?
A. Sinkholing
B. Eradication techniques
C. Continuous monitoring
D. Evidence acquisition
Answer: C. Continuous monitoring
Continuous monitoring helps detect exploitation attempts until a patch is available.
Question 7
The Chief Information Security Officer wants to improve internal security measures by continuously validating and verifying access to the production environment. Which of the following concepts best describes this practice?
A. Secure access service edge
B. Next-generation firewall
C. Zero Trust
D. Privileged access management
Answer: C. Zero Trust
Zero Trust continuously validates and verifies access to resources.
Question 8
Which of the following allows an organization to leverage AI in various forms while protecting business objectives and data?
A. Usage policies
B. Prompt engineering
C. Non-disclosure agreement
D. Incident response policy
Answer: A. Usage policies
AI usage policies govern how AI is used while protecting business objectives and data.
Question 9
A security operations center analyst is using the command line to display specific traffic. The analyst uses the following command:
$tshark -r file.pcap -Y “http or udp”
Which of the following will the command line display?
A. Encrypted web requests and Domain Name System (DNS) traffic
B. Unencrypted web requests and DNS traffic
C. Neither encrypted nor unencrypted web and DNS traffic
D. Both encrypted and unencrypted web and DNS traffic
Answer: B. Unencrypted web requests and DNS traffic
The filter “http or udp” captures unencrypted HTTP and UDP (DNS) traffic.
Question 10
Which of the following network architectures would best implement a perimeter-less network topology?
A. Hybrid cloud networks
B. Secure access service edge
C. Cloud-native computing
D. Content delivery networks
Answer: B. Secure access service edge
SASE provides a perimeter-less architecture by converging network and security in the cloud.
CS0-004 Practice Questions 11-15
Question 11
A new security operations center (SOC) manager joins a team that struggles to meet service-level agreements (SLAs). The alert backlog continues to increase daily. Which of the following will the manager most likely need to do?
A. Automate escalation.
B. Improve the triage processes.
C. Upgrade threat intelligence.
D. Enhance the customer service response.
Answer: B. Improve the triage processes.
Improving triage processes helps reduce alert backlog and meet SLAs.
Question 12
Which of the following should a cybersecurity analyst utilize when a notification is inaccurate?
A. Data enrichment
B. Dashboard creation
C. Threat hunting
D. Alert tuning
Answer: D. Alert tuning
Alert tuning reduces inaccurate notifications.
Question 13
A Chief Information Security Officer (CISO) evaluates a threat heat map and notices a substantial increase in custom scanning and enumeration activities. The CISO wants to gather as much information as possible about the activities targeting the company to help prioritize mitigations. Which of the following solutions is the best way to accomplish this goal?
A. Configuring a honeypot in a separate environment to gather attacker techniques
B. Leveraging canary tokens on all production systems to detect valid intrusion attempts
C. Subscribing to information-sharing and threat intelligence reports for the industry
D. Implementing a web application firewall in front of all applications and having it log attacks
Answer: A. Configuring a honeypot in a separate environment to gather attacker techniques
A honeypot gathers detailed attacker techniques and information.
Question 14
An analyst uses an AI platform to help correlate events. The AI output contains events that did not happen. This results in inaccurate correlations. Which of the following best describes what has occurred?
A. Hallucinations
B. Data exposure
C. Malicious prompts
D. Model poisoning
Answer: A. Hallucinations
AI hallucinations produce false or fabricated outputs.
Question 15
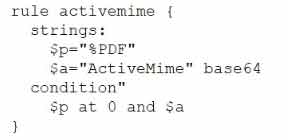
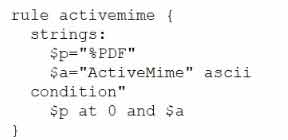
A security analyst must identify documents that contain encoded ActiveMime payloads in a directory containing thousands of files. The analyst runs the following command:
grep -rail ActiveMime *
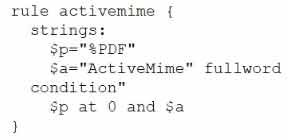
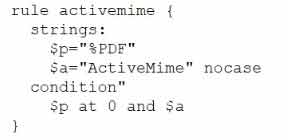
The command returns no output. Which of the following Yet Another Recursive Acronym (YARA) rules should the analyst use to find the suspicious files?
Answer: C
Answer: C
Option C is the correct YARA rule.
CS0-004 Practice Questions 16-20
Question 16
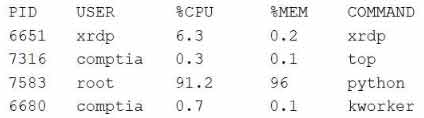
An analyst executes the top command on a Linux system for an unresponsive application and observes the following output:
Which of the following is the most likely cause of this issue?
A. Service disruption
B. Unauthorized software
C. Resource exhaustion
D. Filesystem changes
Answer: C. Resource exhaustion
High CPU or memory usage indicates resource exhaustion.
Question 17
Which of the following is the most difficult for threat actors to change according to the Pyramid of Pain model?
A. Tactics, techniques, and procedures
B. Tools
C. Domain names
D. Internet Protocol addresses
Answer: A. Tactics, techniques, and procedures
TTPs are the hardest for attackers to change according to the Pyramid of Pain.
Question 18
An analyst is assigned to a new cybersecurity improvement project. The analyst wants to better understand the workflow processes and the skill set of the cybersecurity engineers on this task force. The analyst sets up a recurring, weekly conference call. Which of the following best describes the purpose for the conference call?
A. To conduct incident response training
B. To create vendor information sessions
C. To manage and facilitate team coordination
D. To respond to customer requirements
Answer: C. To manage and facilitate team coordination
Recurring calls facilitate team coordination and workflow understanding.
Question 19
A security analyst uses a full pcap solution to extract all traffic from the last two days associated with the 10.213.4.27 file server. This file server is under investigation due to concerns about potential data exfiltration using Domain Name System (DNS) traffic. Which of the following commands should the analyst use to extract any potentially leaked data from the suspicious.pcap file?
A. strings suspicious.pcap | grep 10.213.4.27
B. zeek -r suspicious.pcap ; grep 10.213.4.27 file.log
C. snort -r suspicious.pcap ; grep eve.log 10.213.4.27
D. tcpdump -r suspicious.pcap port 53 and host 10.213.4.27
Answer: D. tcpdump -r suspicious.pcap port 53 and host 10.213.4.27
tcpdump filters DNS traffic (port 53) for the specific host to extract leaked data.
Question 20
An analyst is configuring a security information and event management system to capture fileless malware execution events. Which of the following log files requires additional configuration to accomplish this task?
A. Microsoft-Windows-Crypto-DPAPI/Operational
B. Microsoft-Windows-PowerShell/Operational
C. Microsoft-Windows-UserPnp/DeviceInstall
D. Microsoft-Windows-TerminalServices-LocalSessionManager/Operational
Answer: B. Microsoft-Windows-PowerShell/Operational
PowerShell operational logging must be enabled to capture fileless malware execution.