

Microsoft SC-100 Free Exam Questions 81-100 with Answers
Scenario-based practice questions for the Microsoft SC-100 Cybersecurity Architect exam. Each question includes a clear answer, a plain-English explanation, and a reference link to official Microsoft documentation. Work through them as a diagnostic, then focus your study time on the gaps they reveal.
SC-100 Practice Questions 81-85
Question 81
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
Your on-premises network contains an e-commerce web app that was developed in Angular and Node,js. The web app uses a MongoDB database.
You plan to migrate the web app to Azure. The solution architecture team proposes the following architecture as an Azure landing zone.
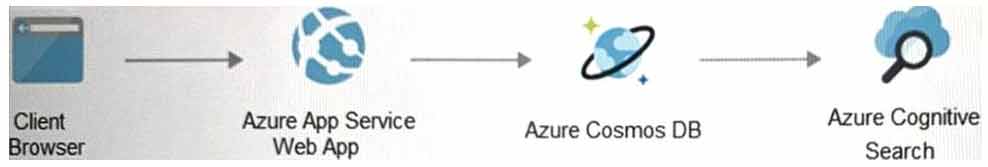
You need to provide recommendations to secure the connection between the web app and the database. The solution must follow the Zero Trust model.
Solution: You recommend implementing Azure Front Door with Azure Web Application Firewall (WAF).
Does this meet the goal?
Reference: Azure Private Endpoint overview
Question 82
You have a customer that has a Microsoft 365 subscription and an Azure subscription.
The customer has devices that run either Windows, iOS, Android, or macOS. The Windows devices are deployed on-premises and in Azure.
You need to design a security solution to assess whether all the devices meet the customer’s compliance rules.
What should you include in the solution?
Reference: Device compliance policies in Microsoft Intune
Question 83
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have an Azure subscription that has Microsoft Defender for Cloud enabled.
You are evaluating the Azure Security Benchmark V3 report.
In the Secure management ports controls, you discover that you have 0 out of a potential 8 points.
You need to recommend configurations to increase the score of the Secure management ports controls.
Solution: You recommend onboarding all virtual machines to Microsoft Defender for Endpoint.
Does this meet the goal?
Reference: Just-in-time VM access in Defender for Cloud
Question 84
Your company has an Azure subscription that has enhanced security enabled for Microsoft Defender for Cloud.
The company signs a contract with the United States government.
You need to review the current subscription for NIST 800-53 compliance.
What should you do first?
Reference: Add a regulatory compliance standard in Defender for Cloud
Question 85
Your company has devices that run either Windows 10, Windows 11, or Windows Server.
You are in the process of improving the security posture of the devices.
You plan to use security baselines from the Microsoft Security Compliance Toolkit.
What should you recommend using to compare the baselines to the current device configurations?
Reference: Policy Analyzer in the Microsoft Security Compliance Toolkit
SC-100 Practice Questions 86-90
Question 86
You have an Azure subscription that is used as an Azure landing zone for an application.
You need to evaluate the security posture of all the workloads in the landing zone.
What should you do first?
Reference: Enable enhanced security features in Defender for Cloud
Question 87
Your company has an Azure subscription that has enhanced security enabled for Microsoft Defender for Cloud.
The company signs a contract with the United States government.
You need to review the current subscription for NIST 800-53 compliance.
What should you do first?
Reference: NIST SP 800-53 R5 regulatory compliance built-in initiative
Question 88
Your company has an Azure subscription that uses Microsoft Defender for Cloud.
The company signs a contract with the United States government.
You need to review the current subscription for NIST 800-53 compliance.
What should you do first?
Reference: NIST SP 800-53 R5 regulatory compliance built-in initiative
Question 89
HOTSPOT
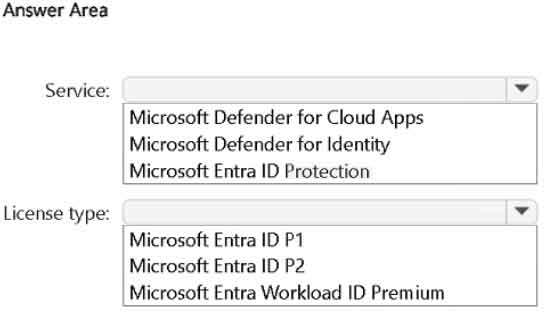
You have a Microsoft Entra tenant that is linked to a Microsoft 365 subscription and an Azure subscription. The tenant contains service principals that are used to access applications in the Azure subscription.
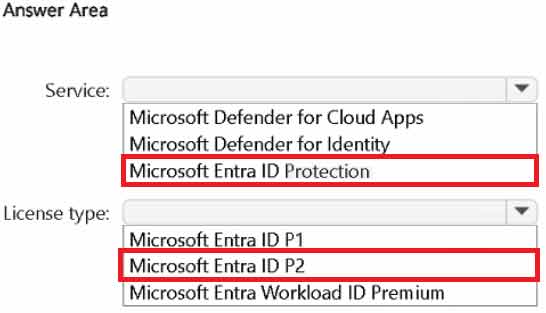
You need to recommend a solution to detect risky sign-ins and other risky activities performed by the service principals in the tenant. The solution must minimize costs.
What should you include in the recommendation? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Reference: Identity Protection risk detections
Question 90
HOTSPOT
Your network contains an Active Directory Domain Services (AD DS) domain named Domain1.
You have a Microsoft Entra tenant.
Domain1 syncs with the tenant by using Microsoft Entra Connect.
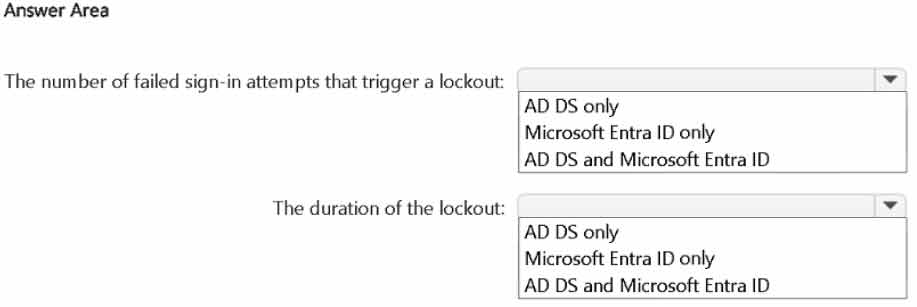
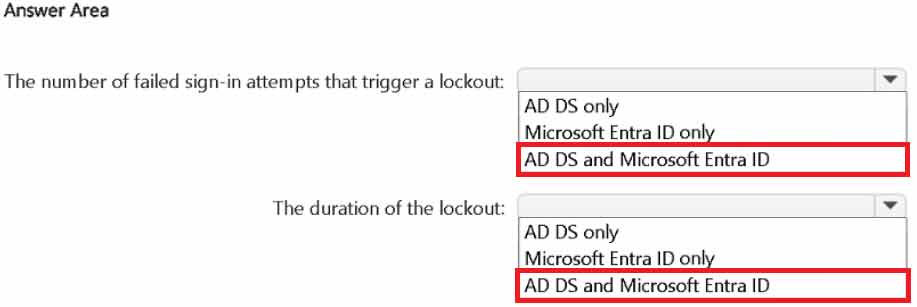
You need to evaluate Microsoft Entra smart lockout by testing the following account lockout considerations:
• The number of failed sign-in attempts that trigger a lockout
• The duration of the lockout
What should you use to test each consideration? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Reference: Protect users from password spray with smart lockout
SC-100 Practice Questions 91-95
Question 91
You have a Microsoft 365 subscription that contains 1,000 Microsoft Exchange Online mailboxes.
Incoming email from the internet is scanned for security threats by using a third-party cloud service.
You are evaluating whether to replace the third-party service with Microsoft Defender for Office 365.
What should you modify to ensure that all the incoming email is scanned by Defender for Office 365 only?
Reference: Mail flow in Exchange Online Protection
Question 92
You have a Microsoft 365 tenant that contains two groups named Group1 and Group2.
You use Microsoft Defender XDR to manage the tenants of your company’s customers.
You need to ensure that the users in Group1 can perform security tasks in the tenant of each customer. The solution must meet the following requirements:
• The Group1 users must only be assigned the Security Operator role for the customer tenants.
• The users in Group2 must be able to assign the Security Operators role to the Group1 users for the customer tenants.
• The use of quest accounts must be minimized.
• Administrative effort must be minimized.
What should you include in the solution?
Reference: Azure Lighthouse overview
Question 93
You have an Azure subscription.
Your company has a governance requirement that resources must be created in the West Europe or North Europe Azure regions.
What should you recommend using to enforce the governance requirement?
Reference: Azure Policy definition structure
Question 94
HOTSPOT
You have a Microsoft 365 subscription that is protected by using Microsoft 365 Defender.
You are designing a security operations strategy that will use Microsoft Sentinel to monitor events from Microsoft 365 and Microsoft 365 Defender.
You need to recommend a solution to meet the following requirements:
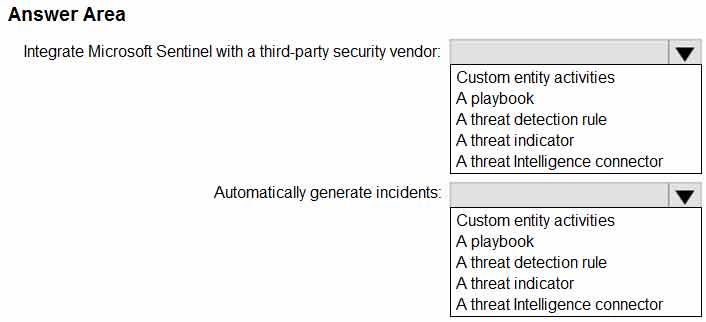
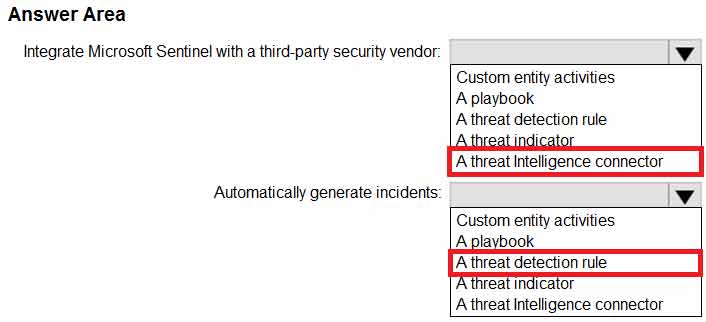
• Integrate Microsoft Sentinel with a third-party security vendor to access information about known malware.
• Automatically generate incidents when the IP address of a command-and-control server is detected in the events.
What should you configure in Microsoft Sentinel to meet each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Reference: Threat intelligence in Microsoft Sentinel
Question 95
You have an Azure subscription that has Microsoft Defender for Cloud enabled.
You need to enforce ISO 27001:2013 standards for new resources deployed to the subscription. The solution must ensure that noncompliant resources are automatically detected.
What should you use?
Reference: Azure Policy definition structure
SC-100 Practice Questions 96-100
Question 96
DRAG DROP
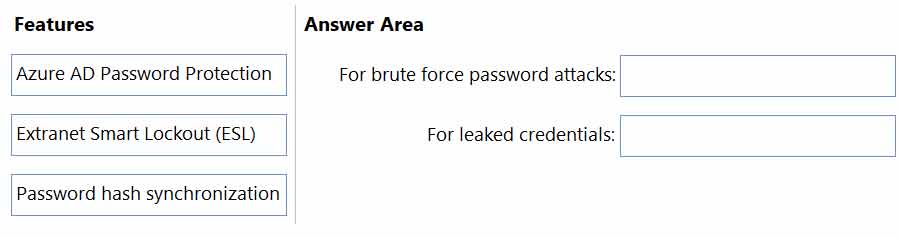
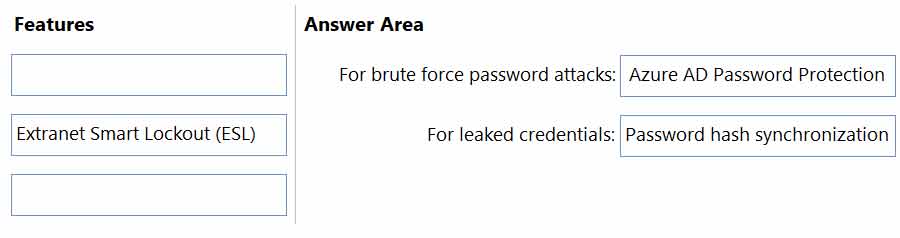
You have a hybrid Azure AD tenant that has pass-through authentication enabled.
You are designing an identity security strategy.
You need to minimize the impact of brute force password attacks and leaked credentials of hybrid identities.
What should you include in the design? To answer, drag the appropriate features to the correct requirements. Each feature may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
Reference: Protect users from password spray with smart lockout
Question 97
HOTSPOT
You are designing the security architecture for a cloud-only environment.
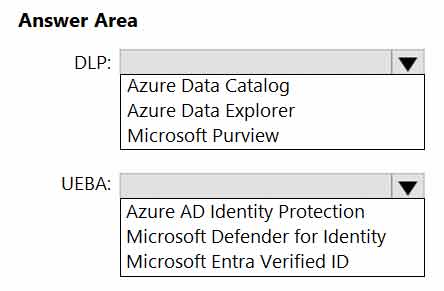
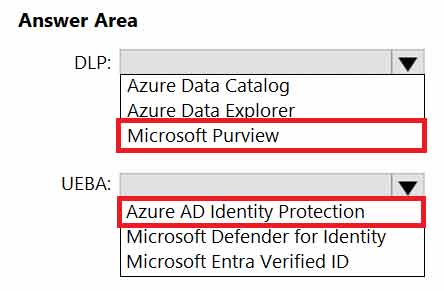
You are reviewing the integration point between Microsoft 365 Defender and other Microsoft cloud services based on Microsoft Cybersecurity Reference Architectures (MCRA).
You need to recommend which Microsoft cloud services integrate directly with Microsoft 365 Defender and meet the following requirements:
• Enforce data loss prevention (DLP) policies that can be managed directly from the Microsoft 365 Defender portal.
• Detect and respond to security threats based on User and Entity Behavior Analytics (UEBA) with unified alerting.
What should you include in the recommendation for each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Reference: Microsoft Defender XDR overview
Question 98
HOTSPOT
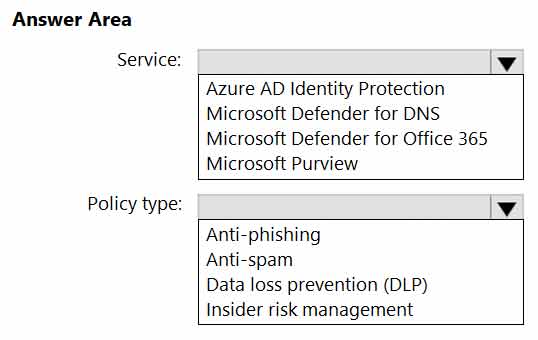
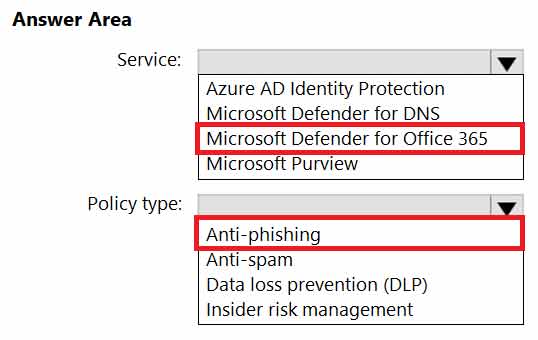
You have a Microsoft 365 E5 subscription that uses Microsoft Exchange Online.
You need to recommend a solution to prevent malicious actors from impersonating the email addresses of internal senders.
What should you include in the recommendation? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Reference: Impersonation protection in anti-phishing policies
Question 99
HOTSPOT
Your network contains an on-premises Active Directory Domain Services (AD DS) domain. The domain contains a server that runs Windows Server and hosts shared folders. The domain syncs with Azure AD by using Azure AD Connect. Azure AD Connect has group writeback enabled.
You have a Microsoft 365 subscription that uses Microsoft SharePoint Online.
You have multiple project teams. Each team has an AD DS group that syncs with Azure AD.
Each group has permissions to a unique SharePoint Online site and a Windows Server shared folder for its project. Users routinely move between project teams.
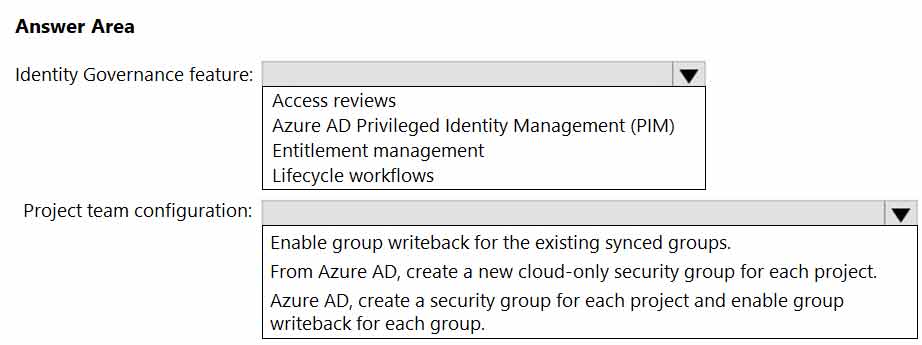
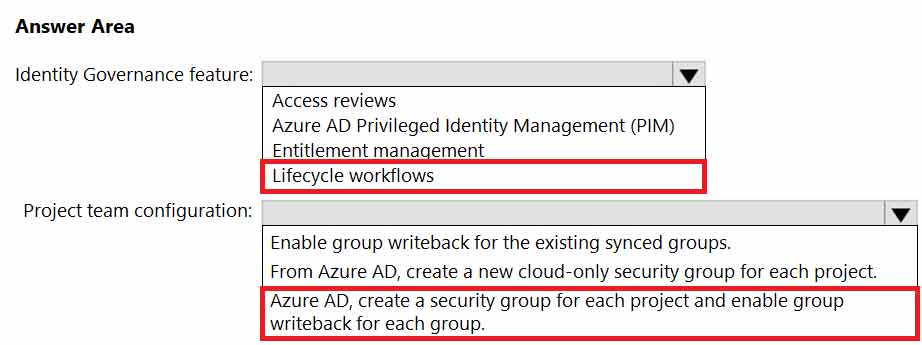
You need to recommend an Azure AD Identity Governance solution that meets the following requirements:
• Project managers must verify that their project group contains only the current members of their project team.
• The members of each project team must only have access to the resources of the project to which they are assigned.
• Users must be removed from a project group automatically if the project manager has NOT verified the group’s membership for 30 days.
• Administrative effort must be minimized.
What should you include in the recommendation? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Reference: Access reviews in Microsoft Entra ID Governance
Question 100
HOTSPOT
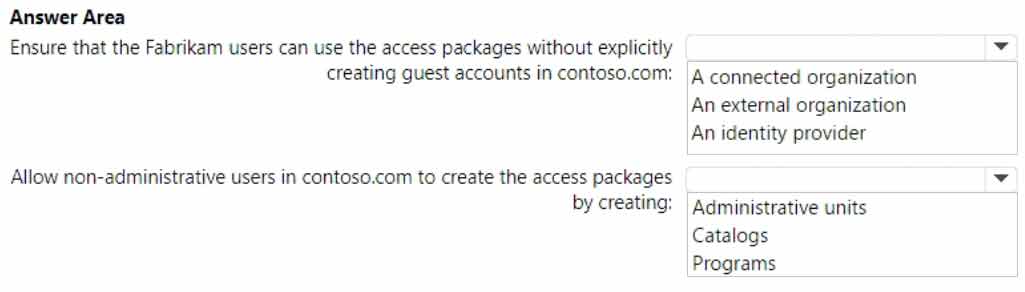
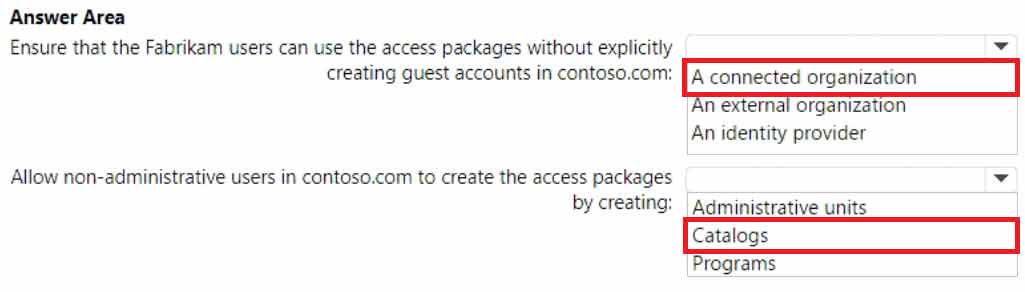
You are designing a privileged access strategy for a company named Contoso, Ltd. and its partner company named Fabrikam, Inc. Contoso has an Azure AD tenant named contoso.com. Fabrikam has an Azure AD tenant named fabrikam.com. Users at Fabrikam must access the resources in contoso.com.
You need to provide the Fabrikam users with access to the Contoso resources by using access packages. The solution must meet the following requirements:
• Ensure that the Fabrikam users can use the Contoso access packages without explicitly creating guest accounts in contoso.com.
• Allow non-administrative users in contoso.com to create the access packages.
What should you use for each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Reference: Microsoft Entra entitlement management overview